

News
Java Security Flaws Surge Sevenfold in 2026. Attacks Don't Follow.
Waratek's State of Java Exploits 2026 finds 5,649 new Java CVEs this year, more than seven times 2025, yet attackers have exploited only 18 of them.
In an era of instant coding filled with AI-generated vulnerabilities, Waratek offers the only compiler-based runtime application tools that report 100% of exploitable vulnerabilities in the pre-production pipeline and block attacks in production against known and Zero Day flaws.
Stop Chasing Vulnerabilities.
Start Fixing Them.
In today’s accelerated development landscape, security teams are often trapped in an endless cycle of reaction-chasing down alerts, triaging false positives, and scrambling to patch vulnerabilities long after code has been deployed.
Waratek disrupts this cycle by offering the industry’s only compiler-based, runtime application security platform. By embedding security directly into the application's runtime, we provide tools that not only find vulnerabilities with precision during the pre-production development pipeline but also instantly block attacks in production against both known and unknown threats. Unlike perimeter defenses, Waratek provides:
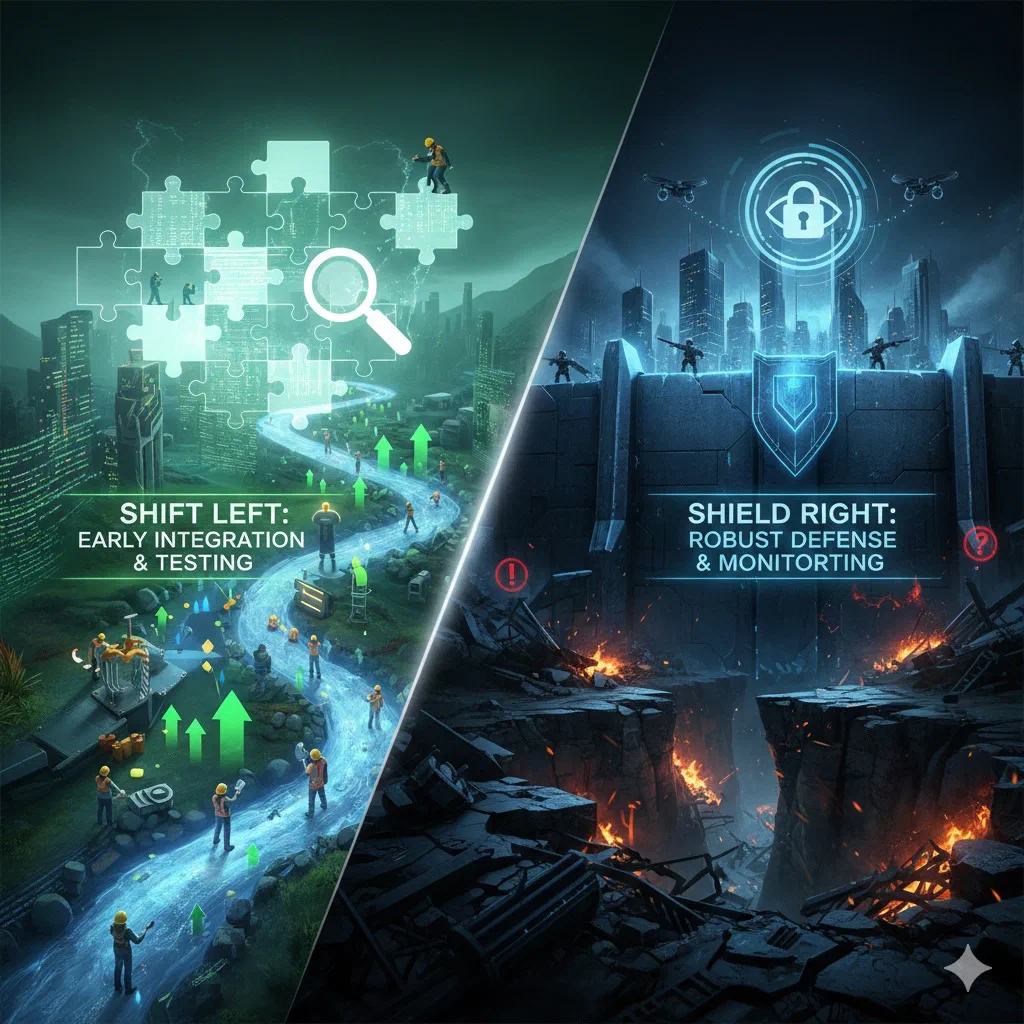
In an era of rapid deployment and sophisticated threats, traditional security testing is no longer enough. Waratek delivers the industry’s only unified Shift Left and Shield Right strategy.
By moving security into the runtime, we eliminate the friction between development and security, providing ultra-accurate test results and instant, immutable protection in production.
News
Waratek's State of Java Exploits 2026 finds 5,649 new Java CVEs this year, more than seven times 2025, yet attackers have exploited only 18 of them.
Paper
A 2026 guide to Oracle PeopleSoft security covering recent critical CVEs, common vulnerability classes, hardening best practices, …
News
Waratek launches AI Phylax at Oracle AI World, a runtime guardian that uses immutable security rules to block attacks on …
News
Waratek's analysis of Oracle's October 2026 CPU: 1,295 patches, six CVSS 10.0 flaws, and renewed ShinyHunters attacks on …

